It’s five o’clock on a Friday night, and as you head onto the highway, you realize that traffic has come to a full and complete crawl. While grumbling to yourself,
As a child, playing hide-and-seek was fun. As the hider, you knew all the best places to avoid being found. As the seeker, you knew your friends well-enough to guess
You’re walking into a cineplex to meet up with a friend you haven’t seen in a few years. However, the movie you agreed to see is showing in three different
In the Brothers Grimm version of Hansel and Gretel, the two children leave a path of breadcrumbs behind as their father brings them deep into the woods. Unfortunately for the
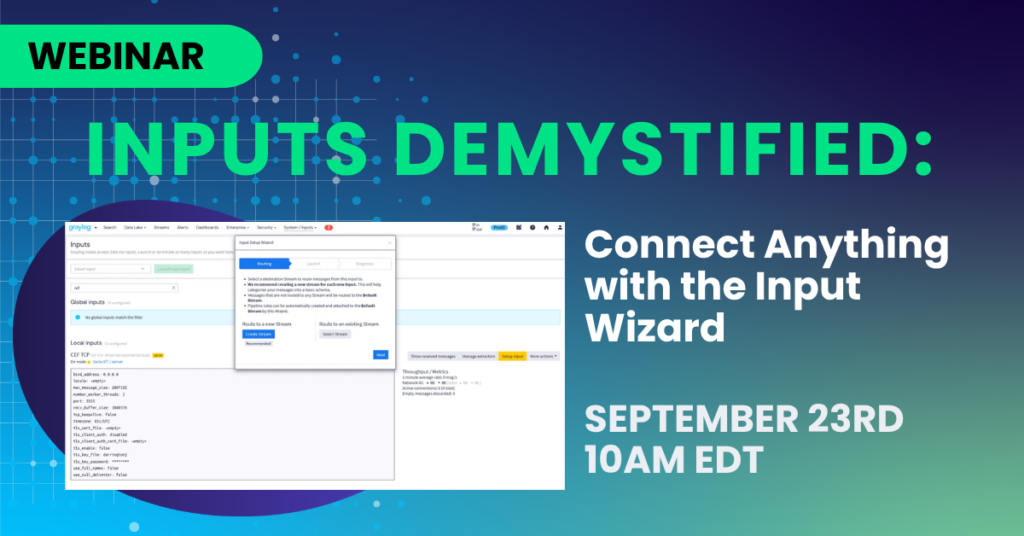
Getting logs into Graylog does not require a PhD in syslog. That is the idea behind our next session in the Getting the Most out of Graylog Open series: Inputs
Free Online Graylog Analyst Training Efficient log management and analysis are crucial for maintaining robust IT infrastructures. To empower IT professionals and enthusiasts with the skills needed to harness
Host-based intrusion detection often lives at the edge of a SOC’s attention, generating a steady stream of file integrity alerts, authentication events, and active response actions that rarely get the
What to Expect? You downloaded Graylog Open. Now what? Part of the Getting the Most out of Graylog Open series, this session walks Open users through a real installation from
Sometimes, driving along an empty, straight stretch of highway can lead you to pay less active attention. As your mind wanders a bit, your car starts slowly drifting toward the
In a famous I Love Lucy episode, Lucy and Ethel take jobs at a chocolate factory, tasked with wrapping each piece of candy as it passes by on a conveyor
When a pipe bursts in your house, the resulting flood is only one symptom of a larger plumbing problem. Until you find that hidden pipe in your wall, you’re going
Email is still one of the most heavily abused paths into an organization, and the server that routes it sits on a mountain of security-relevant data that most teams never
Since its 2018 implementation, the European Union General Data Protection Regulation (GDPR) has been a foundational data protection law that changed how organizations collect, process, and manage sensitive data. The